WordPress Malware Scan & Cleanup Single Site: Complete Hacked Site Recovery & Security Hardening
WordPress Malware Scan & Cleanup Single Site is an emergency site recovery and security hardening package designed to eliminate malicious code, remove SEO spam redirects, clean backdoors, and restore your compromised WordPress website to full health. A hacked website does not just disrupt your daily business operations—it triggers Google search blacklist warnings, causes sudden drops in organic rankings, flags dangerous security warnings in web browsers, and compromises sensitive client data.
Whether your site is suffering from Japanese SEO spam, malicious pharma redirects, hidden admin backdoors, or core file injections, our WordPress Malware Scan & Cleanup Single Site service provides deep database cleansing, theme/plugin core file restoration, and proactive security hardening to ensure your site stays safe and indexed.
Why Immediate Malware Cleanup is Critical for Business SEO
When search engine crawlers detect malicious scripts or forced redirect links on your domain, automated security filters act instantly to protect searchers. Failing to clean a hacked WordPress site immediately leads to severe, long-lasting search engine penalties.
Key Recovery & Security Benefits
-
Google Blacklist & Warning Removal: We clear “This site may be hacked” warnings on Google SERPs and submit formal review requests to Google Search Console and McAfee.
-
Elimination of Malicious Code & Backdoors: Deep file and database scanning to root out obfuscated PHP scripts, rogue admin accounts, and hidden backdoors.
-
Restoration of Search Engine Rankings: Cleaning spam injection pages restores clean crawl paths, allowing search engine bots to re-index your legitimate content.
-
Server & Database Hardening: Implementing strict firewall rules, two-factor authentication (2FA), updated file permissions, and database prefix security.
-
SSL & Browser Trust Restoration: Eliminating browser-level security popups so prospective buyers can browse your WooCommerce shop or service pages safely.
What is Included in Your Malware Cleanup Package?
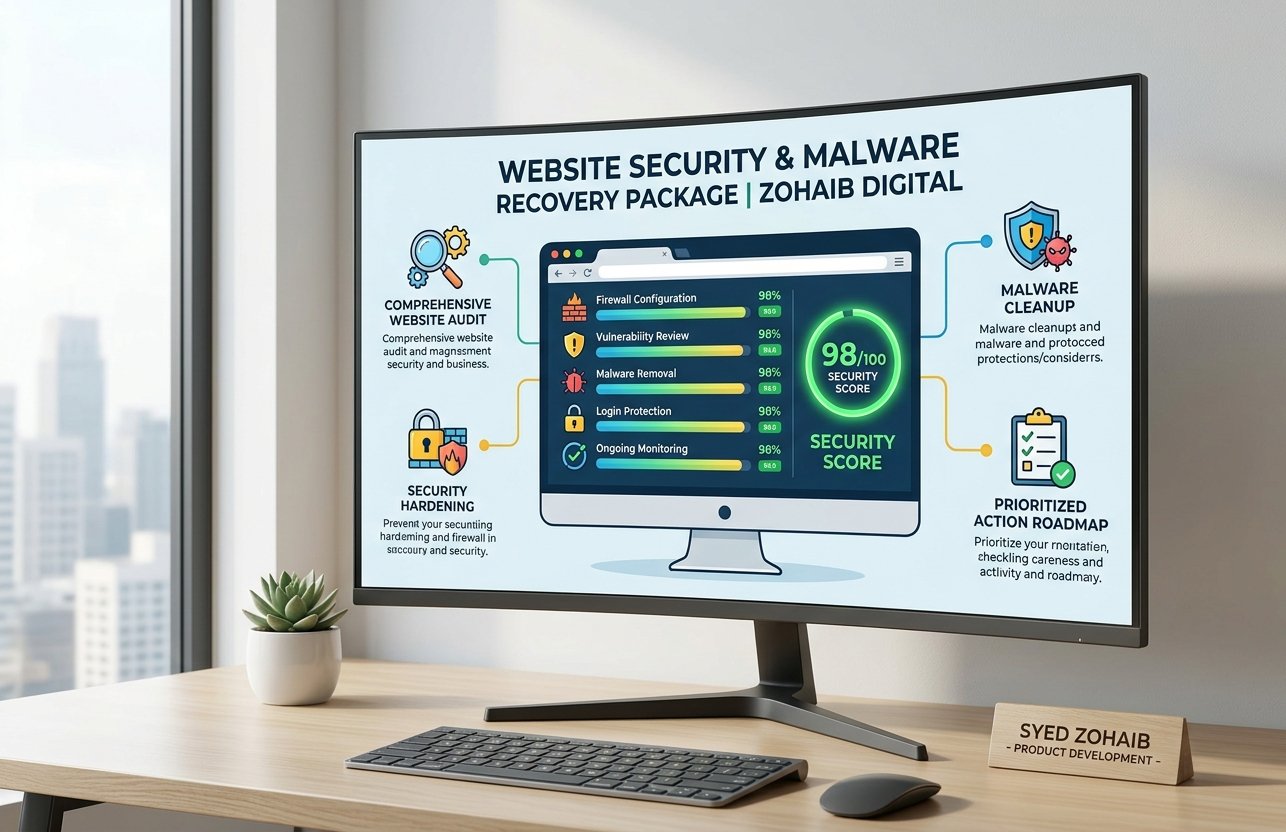
Our emergency cleanup service covers every phase of hacked site recovery, database cleansing, and proactive security shielding:
| Recovery Component | Diagnostic & Execution Scope | Core Security Value |
| Deep Core & File Scan | Complete audit of wp-content, wp-includes, wp-admin, and .htaccess files |
Pinpoints hidden malware scripts and malicious code injections |
| Database & SQL Cleansing | Manual database inspection to remove injected spam tables and rogue admin users | Restores clean database architecture without data loss |
| Core & Plugin Re-installation | Replacement of compromised core WordPress files and plugin repositories with clean copies | Eliminates persistent backdoors embedded in core files |
| Google Blacklist Delisting | Submission of official site review requests to Google Search Console & Security Engines | Removes red browser warnings and restores search visibility |
| Security Hardening Setup | Installation of Wordfence/iThemes Security, firewall rule tuning, and login throttling | Prevents future brute-force attacks and unauthorized file changes |
| Post-Cleanup Backup | Generation of a clean, verified site backup stored securely off-site | Provides an instant rollback point in case of future server issues |
Step-by-Step Emergency Cleanup Workflow
Our agency follows a rigorous 4-phase incident response methodology to recover and secure your WordPress website:
[Phase 1: Quarantine & Backup] ──> [Phase 2: Deep Scan & File Cleansing] ──> [Phase 3: Database & Core Restoration] ──> [Phase 4: Hardening & Blacklist Review]
Phase 1: Site Isolation & Quarantine Backup
We place your site under a temporary security shield and take a full backup of your existing database and files before initiating technical remediation.
Phase 2: Deep File & Server-Level Scanning
We inspect all server directories, checking file signatures against official WordPress checksums to identify modified core files, rogue .htaccess rules, and hidden scripts.
Phase 3: Database Cleansing & Core Replacement
We replace modified core files with fresh, official source files. We query your MySQL database to identify and strip out malicious script tags, iframe injections, and unauthorized admin privileges.
Phase 4: Hardening, Firewall Setup & Blacklist Delisting
We apply advanced security policies, change all database keys, set up Web Application Firewalls (WAF), and submit official reconsideration requests to search security authorities.
Common WordPress Vulnerabilities Found in Hacked Sites
During emergency site restorations, we frequently uncover common security vulnerabilities that leave websites exposed to automated botnets. Here are key entry points our WordPress malware scan & cleanup single site service addresses and closes:
-
Outdated Plugins and Themes: Running outdated extensions with known security vulnerabilities (CVEs) gives hackers instant backdoor entry.
-
Weak Admin Credentials & Brute Force Attacks: Default usernames (such as
admin) paired with weak passwords allow automated bots to guess credentials. -
Insecure File & Directory Permissions: Overly permissive file permissions (like
777on folders) allow malicious scripts to write new files across server directories. -
Nulled or Pirated Premium Extensions: Downloading nulled plugins or cracked themes often introduces pre-packaged backdoors directly into your media library.
For official guidance regarding web security standards, malware remediation, and webmaster guidelines, refer directly to Google Search Central Security Documentation.
Frequently Asked Questions (FAQs)
How quickly can you clean my hacked WordPress website?
Most single-site malware cleanups are completed within 12 to 24 hours, depending on the volume of infected database tables and file directories.
Will I lose my website content, blog posts, or product listings?
No! Our manual cleanup process targets malicious code specifically while preserving your legitimate pages, blog posts, WooCommerce products, and user accounts.
How do you get rid of Google’s red warning screen?
Once all malware and backdoors are removed, we submit a formal security review request through your Google Search Console account. Google typically clears the blacklist banner within 24 to 72 hours.
Explore Our Complementary Digital Growth Packages
Protect and optimize your digital presence by pairing your malware cleanup package with our other specialized agency solutions:
-
Services Hub: Browse our complete catalog of WordPress web design, development, and technical growth packages.
-
WordPress Error Fixing: Rapid resolution for site crashes, white screens of death, broken layout templates, and plugin errors.
-
Technical SEO Services: Site speed enhancements, crawl budget optimization, and canonical tag audits.
-
On-Page SEO Services: Comprehensive multi-page search engine optimization, content structuring, and meta updates.
-
Website Services: Custom WordPress development, Elementor Pro setups, and speed optimization.
-
eCommerce SEO Solutions: Targeted optimization and security setups for WooCommerce stores.
Reviews
There are no reviews yet.